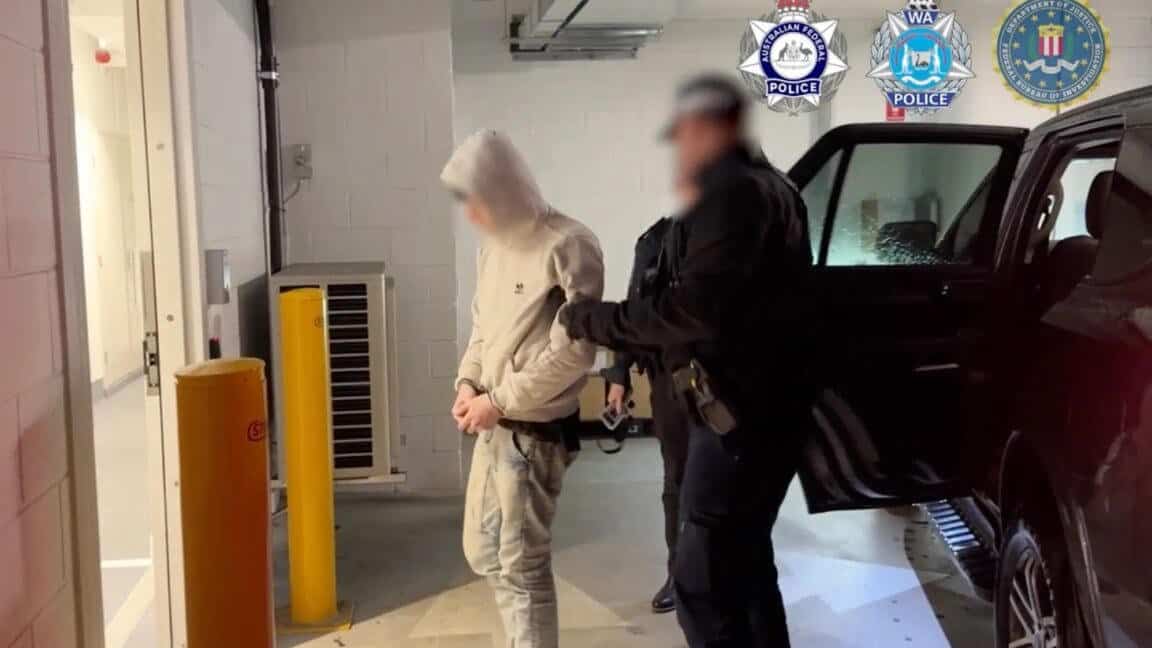

Nine months. More than 1,000 compromised organizations. And it ends, allegedly, in two coastal towns outside Perth.
The Australian Federal Police said Wednesday it arrested two men and charged them with 14 offenses tied to TeamPCP, the hacking crew that spent most of this year pushing self-spreading malware through open source software packages. The AFP didn’t name them. It said only that they lived in Cottesloe and Mandurah, in Western Australia.
KrebsOnSecurity, citing a lengthy investigation, published what it reports are both defendants’ names, along with a detailed account of their lives and the mistakes that led to their downfall.
The worm that rode your build pipeline
TeamPCP has been a problem for law enforcement and security teams worldwide since it surfaced in December. Its signature move was the supply chain attack, and it ran that play over and over.
The group laced open source software with malware that jumped from one package to the next on its own. The target wasn’t your laptop. It was the CI/CD pipeline, the automated machinery organizations use to build, update and ship software fast.
Once a package or tool was compromised, the worm, dubbed Shai-Hulud, attached itself to that package’s future updates. Developers pulled the poisoned versions, ran them through their own CI/CD platforms, and their software got compromised too. Repeat.
What made it viral was a separate piece that scraped credentials for other packages out of the memory of infected hardware. With those credentials in hand, TeamPCP members went and infected those packages as well.
Trivy fell, and everything downstream fell with it
The clearest example of how ugly this gets: the group compromised Trivy, the vulnerability scanner. As reported earlier this month, that single compromise spread to downstream packages including KICS, the Telnyx Python SDK and LiteLLM. Their developers had run either a poisoned version of Trivy or another package that had.
The initial Trivy compromise resulted in the theft of terabytes of credentials and other private data. Terabytes. From a tool whose entire job is finding security problems.
A smart contract as a takedown-proof phone home
Most malware dies when someone seizes its command server. Shai-Hulud was built to survive that.
It used a form of smart contract known as an Internet Computer Protocol-based canister, which let the worm look up control servers through URLs that could be swapped out at any moment. Infected machines checked in with the canister once every 50 minutes.
That’s a genuinely unusual design choice, and it’s the part of this campaign security teams should be reading about most closely. You can’t file an abuse report against a canister the way you can against a hosting provider.
Sloppy operators with very good tools
Here’s the tension in this story. TeamPCP built something technically nasty and durable, and then, according to Brian Krebs of KrebsOnSecurity, its members lacked the operational discipline that usually accompanies a hacking group with that level of accomplishment.
Krebs, citing Aikido Security researcher Charlie Eriksen, reported that hackers operating at that level have traditionally needed to spend significant time researching techniques, tailoring and debugging code, and standing up the infrastructure to pull a campaign like this off.
“LLMs have compressed that gap significantly,” Eriksen told Krebs.
That’s the line worth sitting with. The capability gap that used to separate skilled operators from ambitious amateurs is the thing that kept campaigns like this rare. The operational security gap, apparently, is still wide enough to get you arrested.
What the men are facing
Australian authorities say that if convicted, one of the men faces more than 20 years in prison. The other faces more than 10.
If you run a CI/CD pipeline, the practical takeaway isn’t about the arrests. It’s that a scanner you trusted stole terabytes of credentials from its own users, and the credentials it grabbed became the fuel for the next round of infections. Rotate anything that touched a compromised build. Assume the worm already read it.